
How to Set up Security Settings
Last updated
If you are a team admin, you can control the settings for your team from the XQ Dashboard.
- Log in to the Dashboard.
- Under Settings, you’ll find Security.
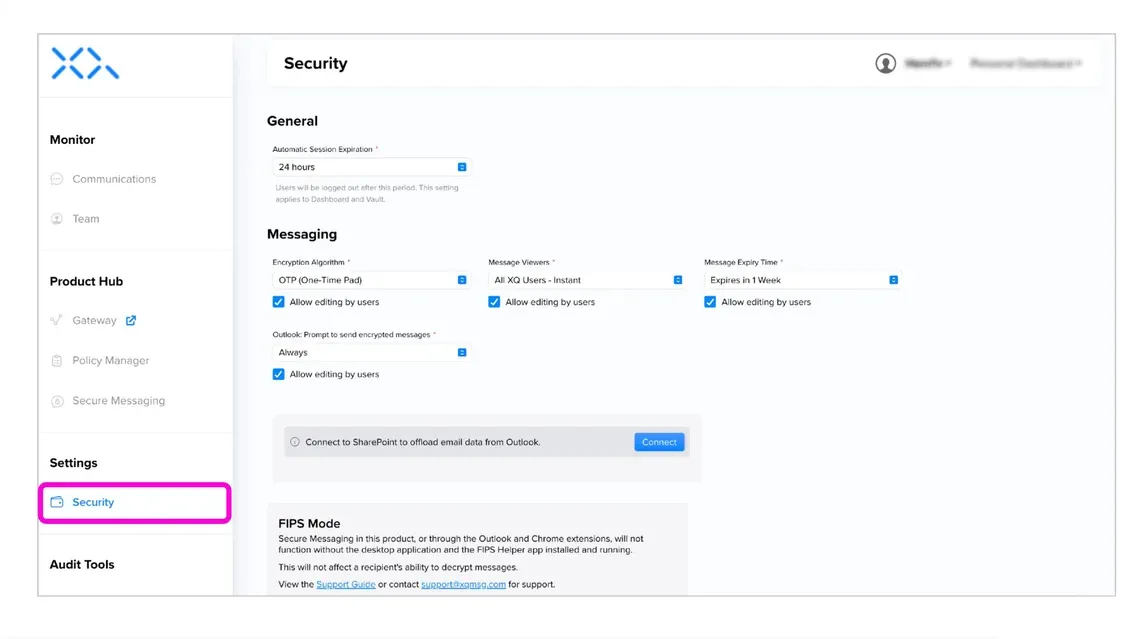
Available settings
Section titled “Available settings”General
Section titled “General”- Automatic Session Expiration: You can choose automatic session expiration for team members using XQ. This allows for greater compliance and flexibility, with options ranging from 30 minutes to 1 month.
Messaging
Section titled “Messaging”-
Encryption Algorithm: You can choose between OTP (One-Time-Pad) and AES-256 GCM. Unchecking the box means that you don’t allow team members to change the encryption algorithm individually.
-
Message Viewers: Choose who can decrypt messages your team sends. Messages are encrypted with either option.
- Recipients Only – Authenticated (recommended): only the sender and the people named in the To, CC or BCC fields can decrypt the message, after signing in to XQ.
- All XQ Users – Instant: anyone who is signed in to XQ can decrypt the message, including people it’s forwarded to.
Unchecking the box means that you don’t allow team members to change the message viewers individually.
-
Message Expiry Time: You can choose any expiration time from 1 hour to 7 years. Unchecking the box means that you don’t allow team members to change the expiration time individually.
-
Outlook: Prompt to send encrypted messages (in the XQ Outlook Enterprise add-in, users see this setting as Always Confirm Insecure Send): You can choose between Always and Never. When set to ‘Never’, users will not see the pop-up box asking them if they want to send the message with or without encryption. Unchecking the box means that you don’t allow team members to change this setting individually.
-
Vault Sharing & Offloading – Connect the SharePoint site where encrypted email content and externally shared Vault files are stored. See Configuring Offloading, External Sharing and Secure Intake.
-
FIPS Mode
- CMMC customers must deploy XQ’s Secure Email extensions in a specific way to ensure they meet Federal Information Processing Standards Publication (FIPS) security standards.
- You can enable FIPS mode by clicking the Enable button. (NEEDS UPDATING)
Vault Access Restrictions
Section titled “Vault Access Restrictions”- By default, when a file is added to Vault, any member of your XQ team with a Vault license, who has permission to access the file, can decrypt it. This setting allows you to have control over the default settings for determining who can decrypt files in a Vault. Please note that this setting relies on the setup of user groups with Microsoft Entra, which you can learn more about here. (NEEDS UPDATING)
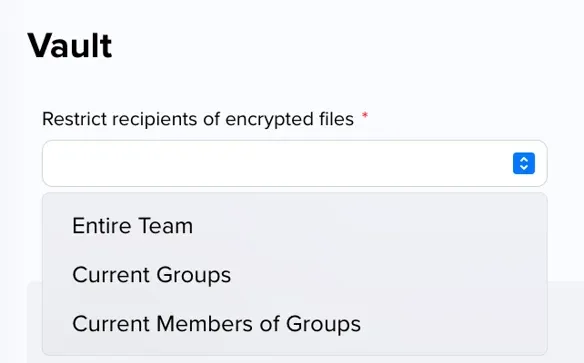
- Entire Team: Adding a file to Vault in this mode, will mean that any licensed member of your team will be able to decrypt Vault files. For example: If I create a Vault location in Sharepoint and add a file, any licensed member of my XQ team, who is also shared in Sharepoint, can decrypt the file.
- Current Groups: Adding a file to Vault in this mode, will mean that the file is decryptable by the groups that I’m a part of at the time of adding. For example: If a user is in two groups, then the files will be decryptable by those groups. Note: If you update the members of these groups, the new members will be able to decrypt the files.
- Current Members of Groups: Adding a file to Vault in this mode will mean that the file is decryptable by only those who are members of the group that I’m a part of at the time of adding. For example: if a user is in two groups, then the files will be decryptable by the members of each of those groups. Future updates to those groups will not be reflected in who can decrypt that file.
© Copyright XQ Message Inc. · FAQ