
Creating Data Loss Prevention and Data Access Control Policies for CMMC Compliance
Last updated
Data Loss Prevention (DLP) and Data Access Control (DAC) Policies are custom rules that trigger specific actions when emails are sent or opened. This article provides guidance on creating policies and examples of best practices.
Access the Policy Manager
Section titled “Access the Policy Manager”Using XQ’s Policy Manager, you can configure DLP and DAC Policies right from your team’s XQ Dashboard. Use the following steps to access the Policy Manager in your dashboard:
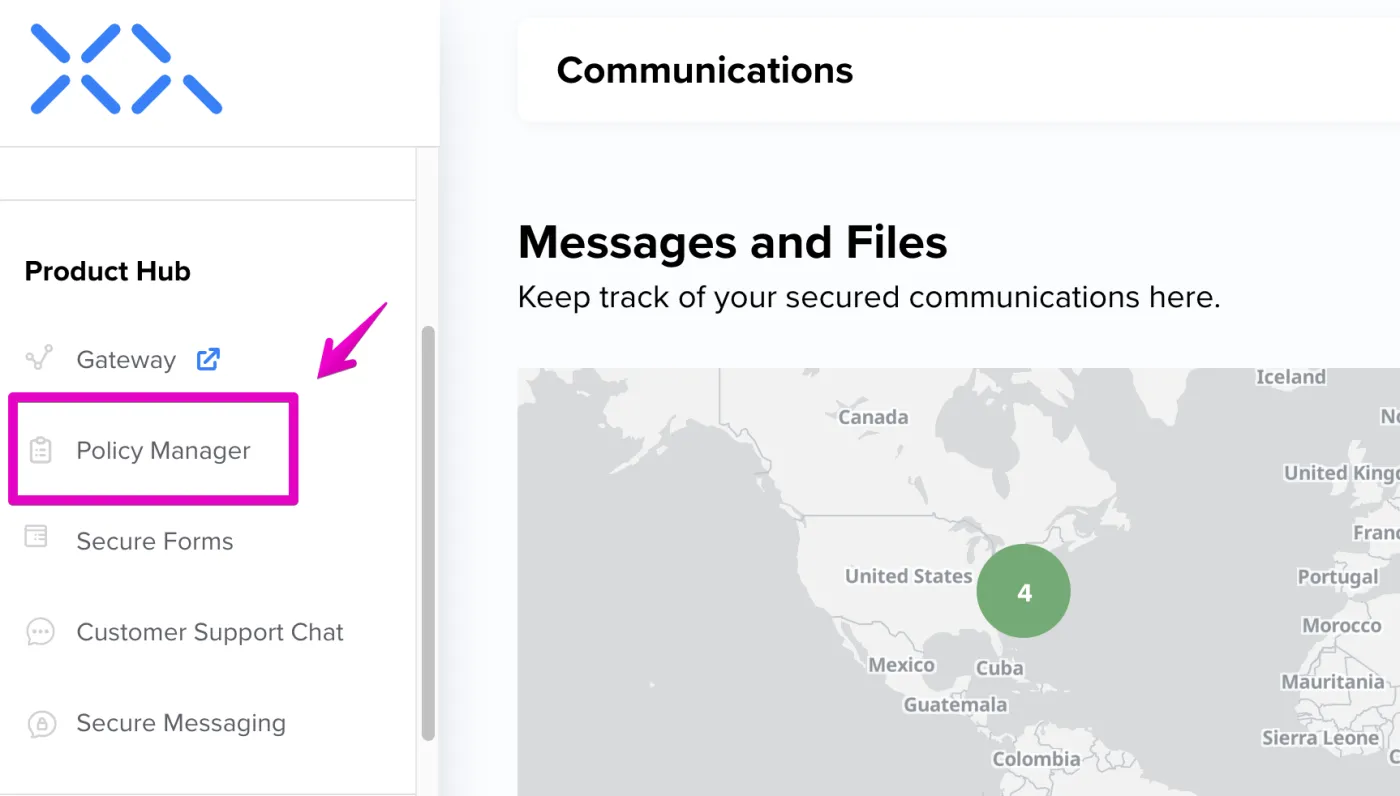
- In the XQ Dashboard, click Policy Manager in the left-hand navigation bar.
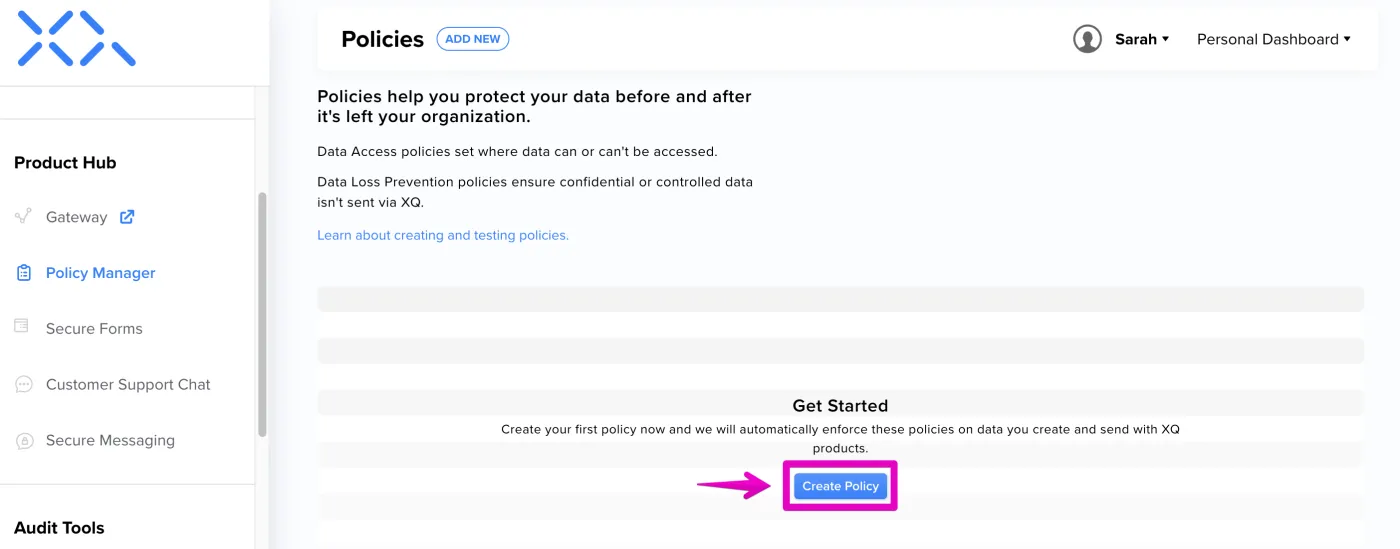
- Click Create Policy to launch the New Policy page.
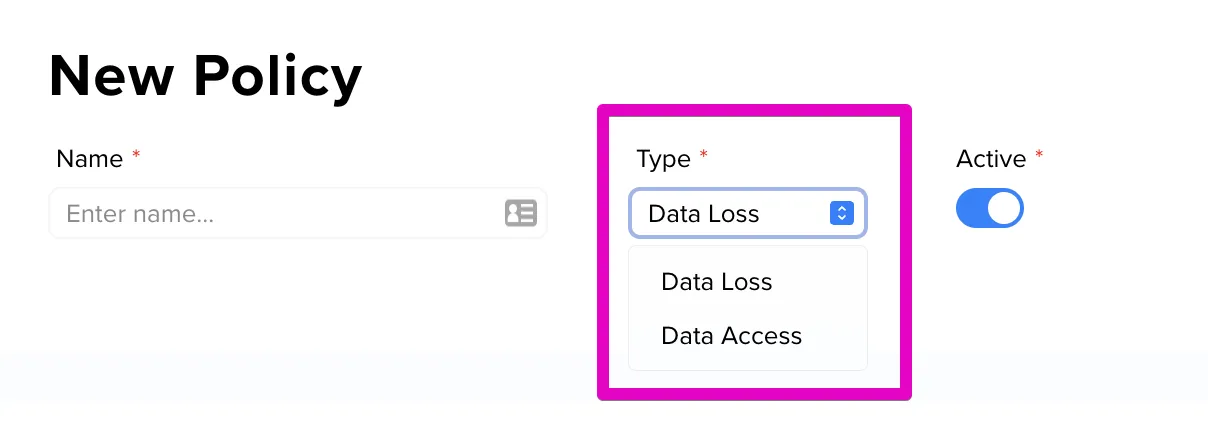
- On the New Policy page, use the Type drop-down menu to choose your policy type. The available types are Data Loss and Data Access.
CMMC Policy Pack
Section titled “CMMC Policy Pack”To make it easier for you to begin implementing CMMC policies, we have created a CMMC Policy Pack which you can simply add to your existing policies and activate.
- Login to your Dashboard and click on Policy Manager.
- Click on Add Policies in the CMMC Policy Pack section; two new policies will appear in the policies list.
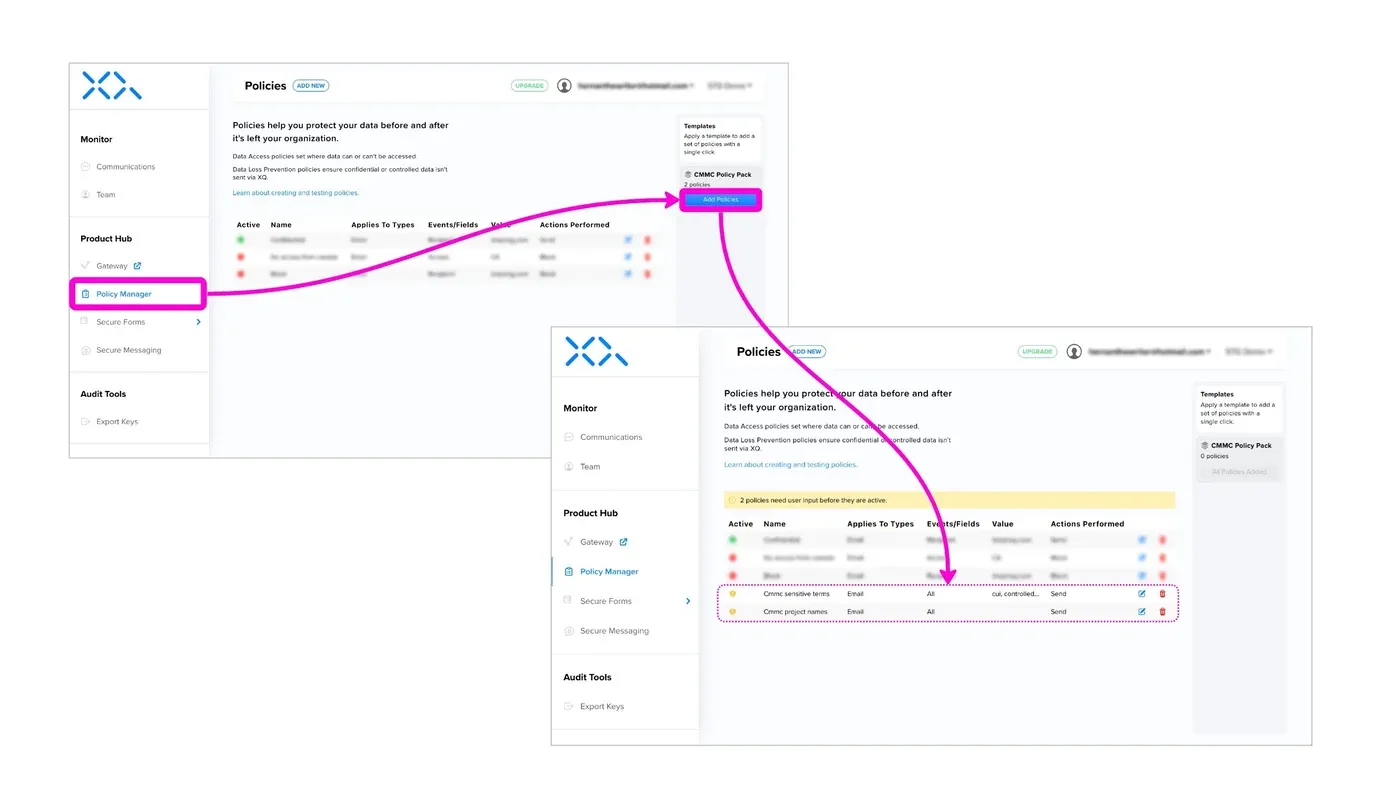
- To activate the CMMC Sensitive Terms policy, click on the Edit button next to it. In the page that opens, turn on the Active toggle and then click Update Policy.
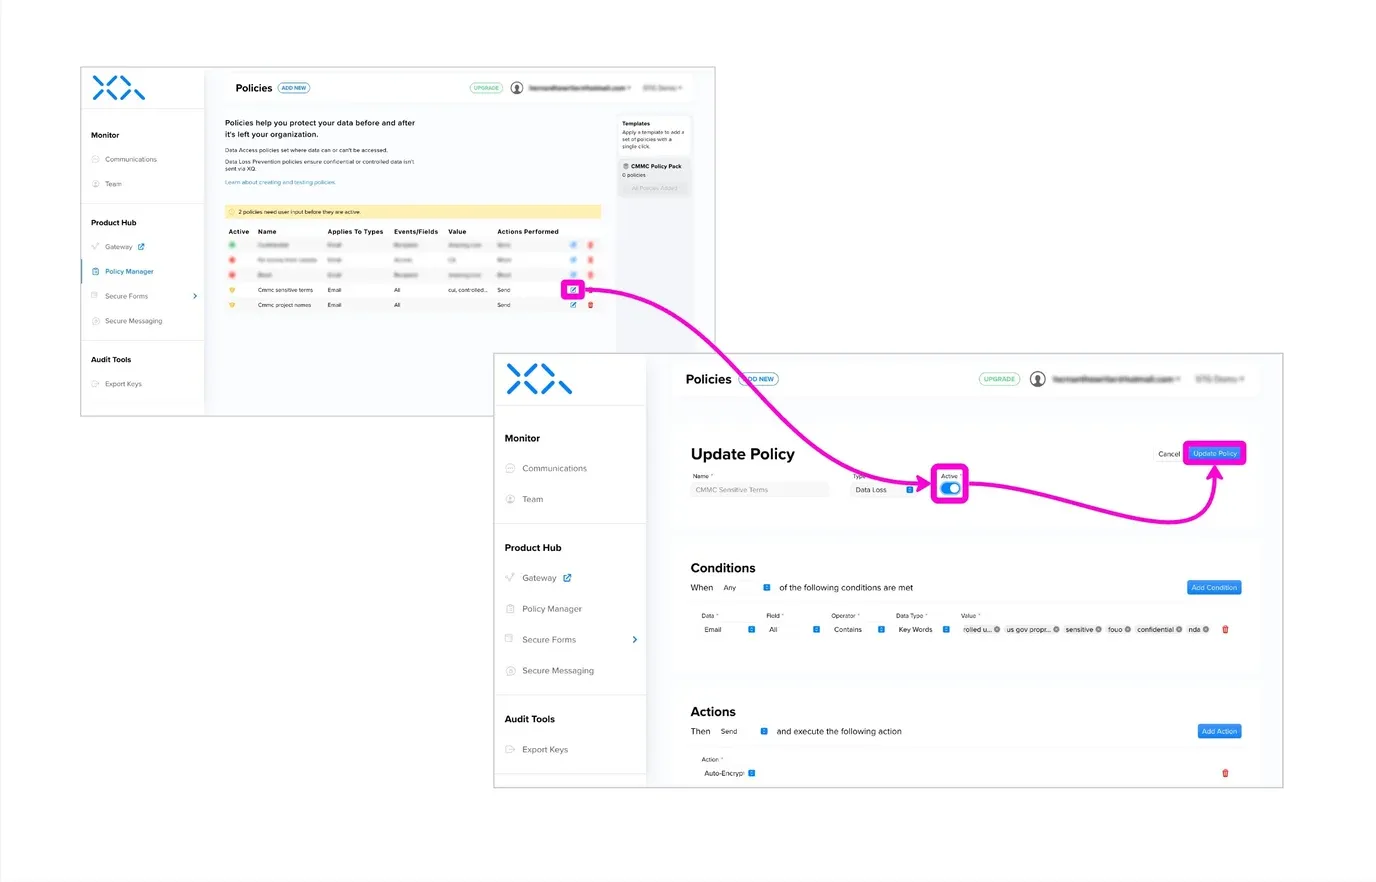
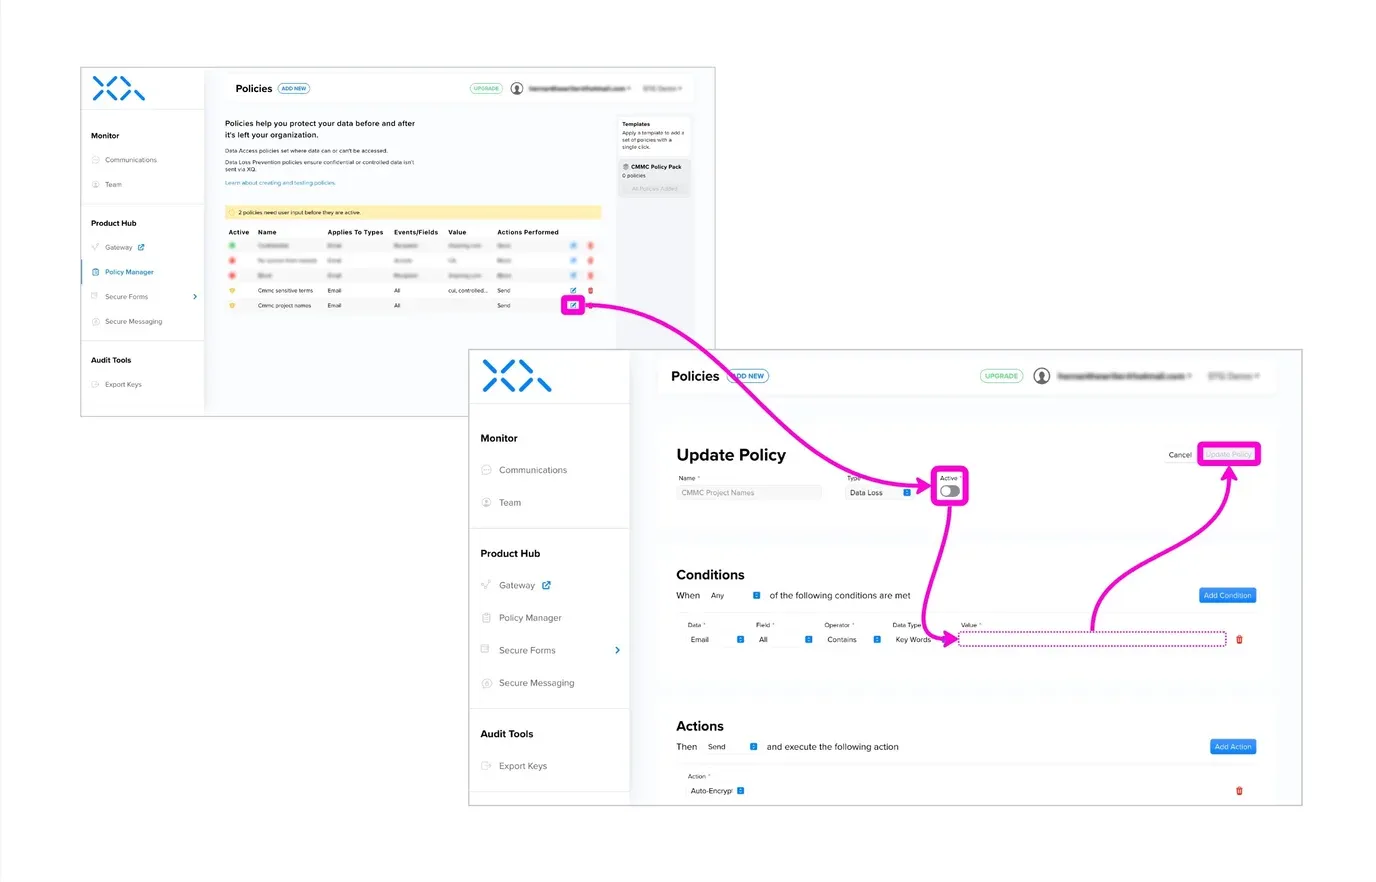
- To activate the CMMC Project Terms policy, click on the Edit button next to it. In the page that opens, turn on the Active toggle, fill out the Value field with the name of the projects that include Controlled Unclassified Information (CUI), and then click Update Policy.
Create Data Loss Prevention Policies
Section titled “Create Data Loss Prevention Policies”Creating Data Loss Prevention (DLP) Policies in XQ ensures the protection of controlled unclassified information (CUI) using automated encryption. With XQ, you can secure your data anywhere it travels.
DLP Policies play a crucial role in meeting CMMC compliance requirements:
- Help companies fulfill multiple NIST 800-171 requirements.
- Enable companies to identify the types of data that require encryption.
- Allow companies to create custom profiles and rules for different types of data.
Create a new policy
Section titled “Create a new policy”Use the following steps to create a Data Loss Prevention (DLP) Policy:
- Launch the Policy Manager in your XQ Dashboard and click Create Policy. If you have already created a policy previously, click the ADD NEW button at the top of the page.
- On the New Policy page, name your policy for future reference and select Data Loss from the Type drop-down.
- Choose your policy’s Conditions. Conditions control which criteria must be met to activate your policy. You can choose between these options:
- Data – Choose Email or Vault. Vault policies match on file names; for example, label any file whose name contains “CUI”.
- Field – What field is being referenced in the email? You can choose whether to reference a recipient or the contents within the message itself.
- Operator – Select the available operator from the drop-down. The operator works by triggering your policy if the Data Type includes your chosen Value. Operator options change depending on the field you choose.
- Data Type – Choose whether to allow or restrict email access based on your chosen Field. The options will change depending on the field you choose. For example, if your field is Recipients, you can choose between Domain and Email Address. If your field is Body, you can choose between Keywords and Pattern.
- Value – Depending on your chosen Data Type, enter a value or select from the dropdown list.
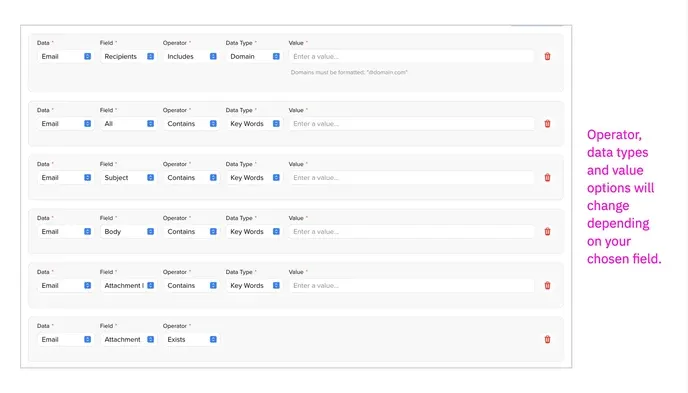
- You can add more conditions by clicking Add Condition in the top-right corner. If you have more than one condition, you can choose whether All or Any conditions are met to then trigger your action. You can also add more than one condition if necessary.
- Choose whether to Send or Block the message. For example, if you want to prevent team members from sending messages containing specific keywords, select Block.
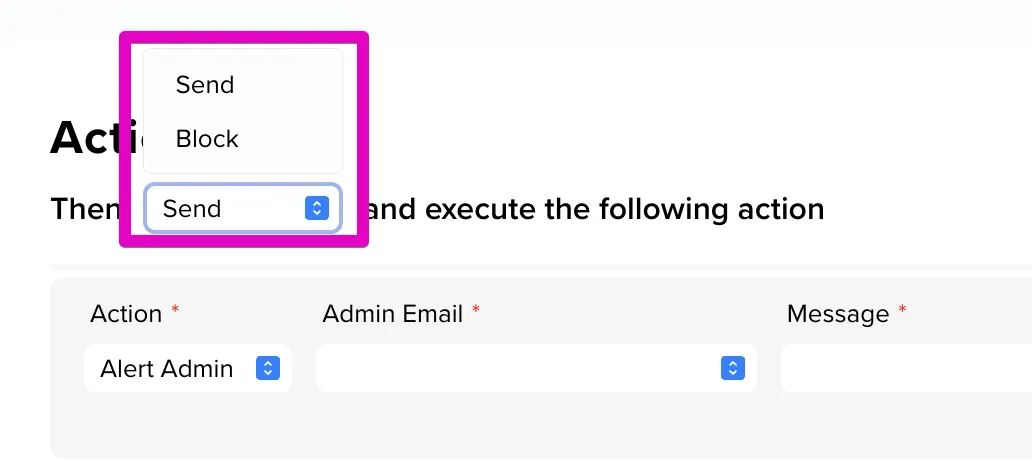
- Then, choose to execute any of the following actions:
- Alert Admin – Emails an admin on your XQ team when the policy is triggered, to report a possible policy violation. Choose the admin from the Admin Email list, which shows the admins on your team, and write the message.
- Notify User – Shows the user a message when the policy is triggered: for example, that they may be violating a policy, or that they should consider encrypting. You can customize the message.
- Log – Log this event in the event log. You can customize the message included in this log.
- Auto-Encrypt – Automatically encrypts the message. It will only appear if the policy action is to send.
- Label Metadata – Adds a label to the data. Data Access policies can then use the label to control who can open it. Emails that match the rule are also auto-encrypted, because labels are only applied to encrypted email. See Labels and Encrypted Data.
Best practice recommendation: Auto-encryption
Section titled “Best practice recommendation: Auto-encryption”To achieve CMMC compliance with Data Loss Prevention (DLP) Policies, we recommend creating auto-encryption policies in XQ. Auto-encryption policies allow you to create criteria using keywords or specific conditions. This eliminates the chance of human error and ensures that all sensitive information is properly encrypted before being sent.
For CMMC compliance, we recommend using the following keywords for your auto-encryption policy:
- CUI
- Confidential
- Controlled
- Classified
- FAO
- Invoice
- JADC2
- NDA
You can use additional keywords to ensure your auto-encryption policies are thorough and effective. The more keywords and conditions you add, the stronger your auto-encryption policies are. We recommend discussing your auto-encryption keywords with your CMMC assessor to ensure compliance with NIST 800-171 requirements.
The following example provides an example of an auto-encryption policy that uses keywords:
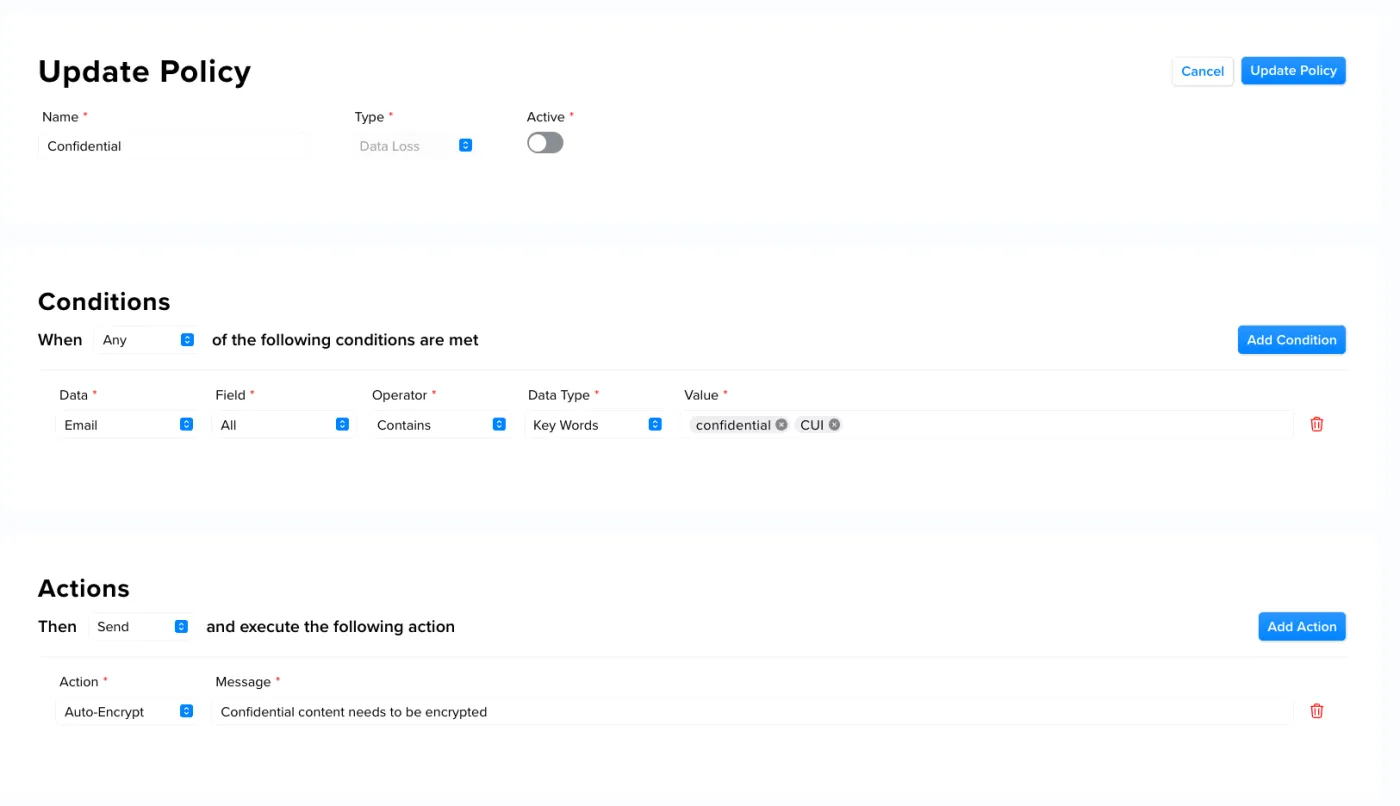
As an additional measure to ensure the security of sensitive information, we suggest automating the encryption of all email attachments. This guarantees that all attachments are always protected by encryption, regardless of their contents.
Create Data Access Policies
Section titled “Create Data Access Policies”Data Access Control (DAC) policies empower the system administrator to set rules for accessing a resource. These rules are established by assigning permissions to designated users. With DAC policies, the administrator can determine who can access the resource and the level of access they are permitted.
DAC Policies play a crucial role in meeting CMMC compliance requirements, as they:
- Help companies fulfill multiple NIST 800-171 requirements.
- These policies provide administrators the ability to establish who is authorized to access a resource and the actions they are allowed to perform with it.
Create a New Policy
Section titled “Create a New Policy”- Launch the Policy Manager in your XQ Dashboard and click Create Policy If you have already created a policy previously, click the ADD NEW button at the top of the page.
- On the New Policy page, name your policy for future reference and select Data Access from the Type drop-down.
- Choose your policy’s Conditions. Conditions control which criteria must be met to activate your policy. You can choose between these options:
- Data – For Data Access Policies, choose Email or Vault.
- Event – For now, you can only choose Access.
- Operator – Choose to trigger your policy if the Data Type is From or Not From a country or IP address.
- Data Type – Choose what to allow or restrict access by: Countries, IPs, or Labels.
- Value – Depending on your chosen Data Type, you can select countries from the dropdown, or you can input an IP address or an IP range.
Use the following format for IP: 192.0.0.1-192 or 192.0.0.0/24 or 192.0.0.*
- Choose whether to Allow or Block if your conditions are met.
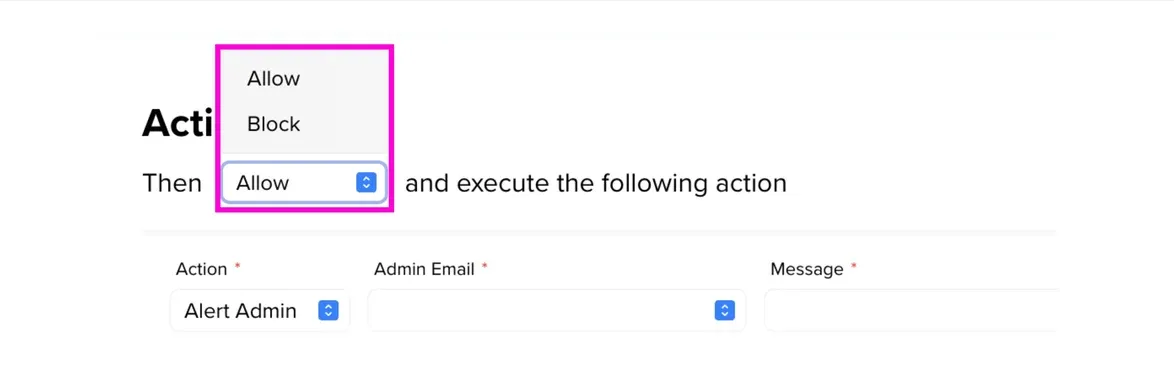
- Choose an Action. The available options include:
- Alert Admin – Emails an admin on your XQ team when the policy is triggered, to report a possible policy violation. Choose the admin from the Admin Email list, which shows the admins on your team, and write the message.
- Notify User – Shows the user a message when the policy is triggered: for example, that they may be violating a policy, or that they should consider encrypting. You can customize the message.
- Log – This action logs this event in the event log. You can customize the message included in this log.
Best practice recommendation: Location-based restriction
Section titled “Best practice recommendation: Location-based restriction”Location-based restriction policies enable you to limit access to resources based on geographical location. These policies prevent unauthorized individuals located outside the designated geographical location from accessing the resource.
This example shows a location-based restriction policy that restricts data access from outside the United States:
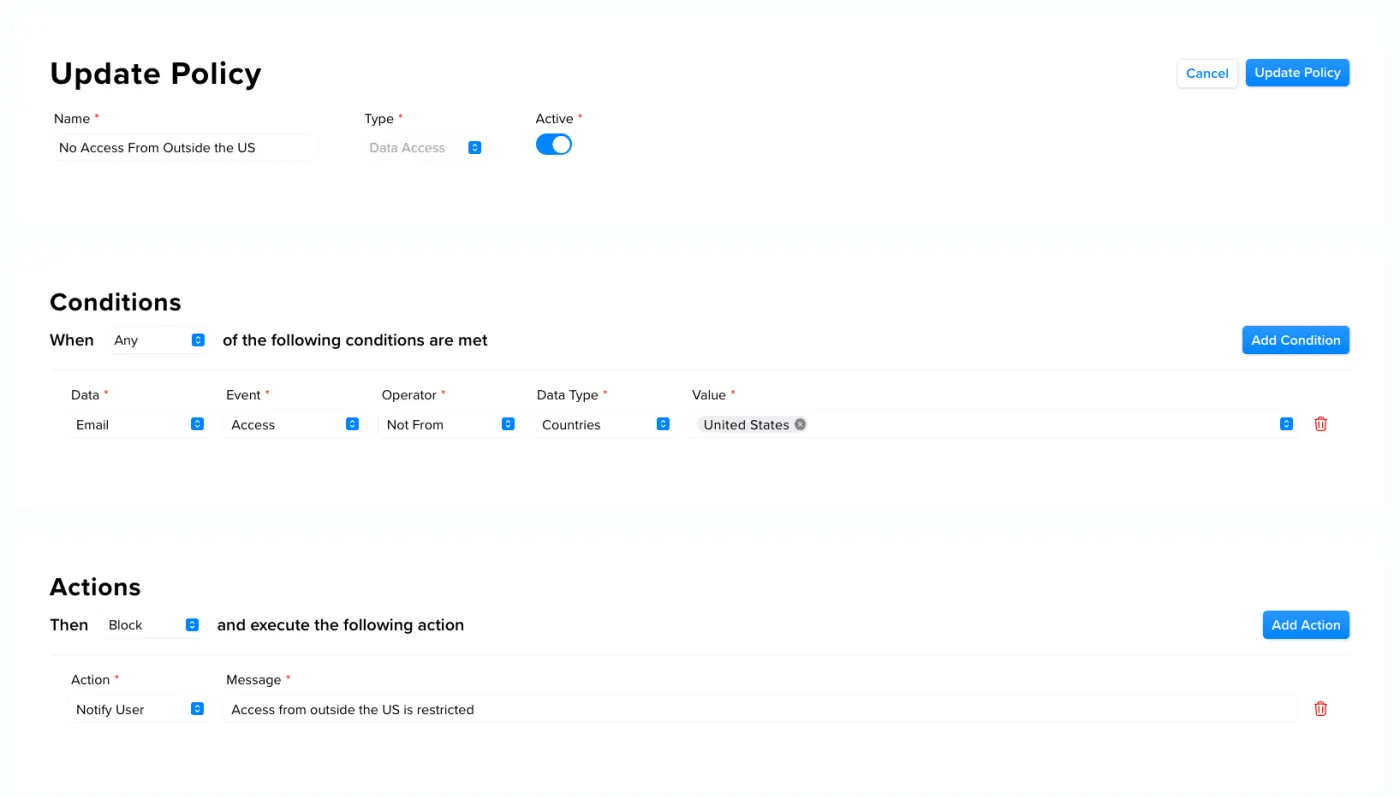
Best practice recommendation: IP address restriction
Section titled “Best practice recommendation: IP address restriction”Further limiting access through IP address restrictions provides a more secure way of controlling user access. When implementing this type of policy, specific IP addresses are designated as authorized for accessing a resource. Attempts to access data from an unapproved IP address will be blocked.
This example shows an IP address-based restriction policy that restricts data access to one authorized IP address:
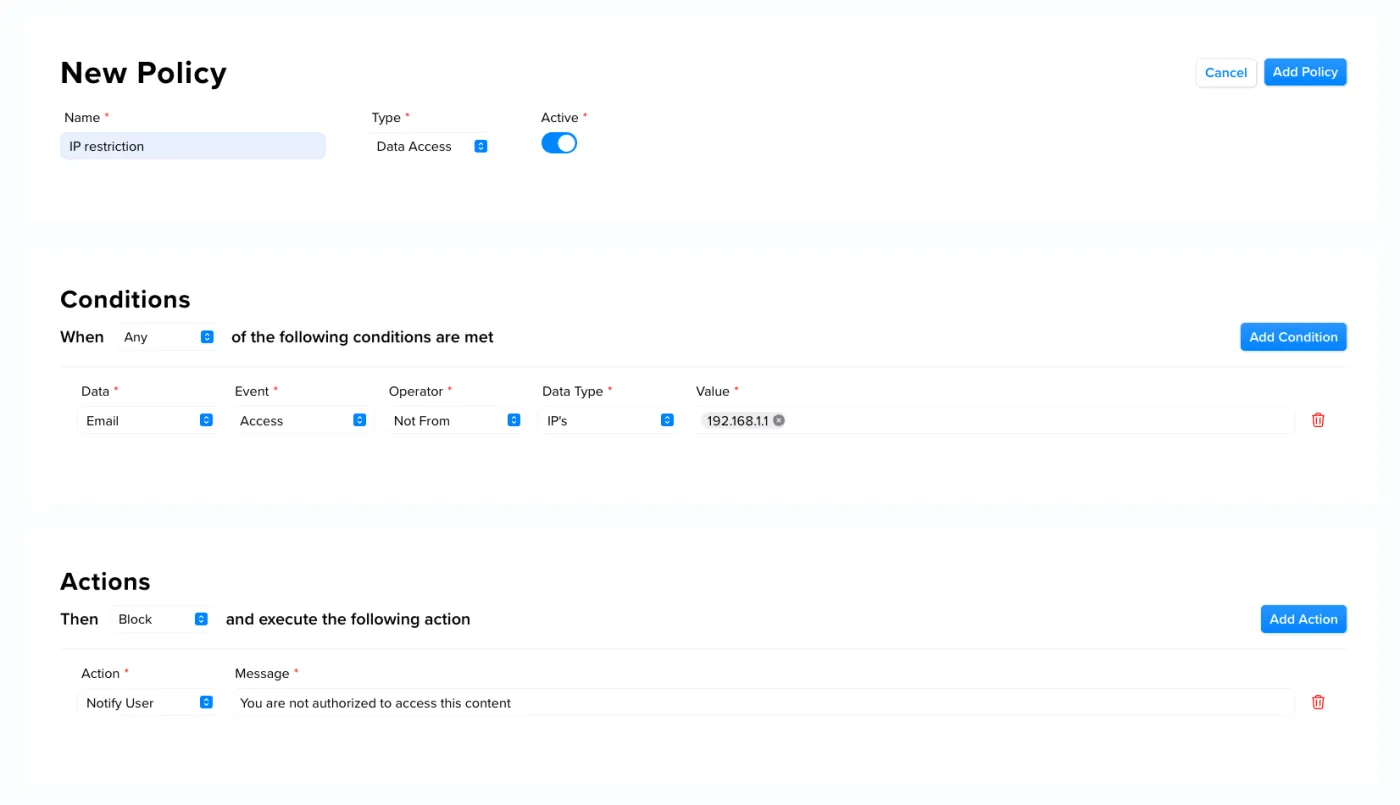
© Copyright XQ Message Inc. · FAQ